Secure communication infrastructure for applications operated by different teams.
Quantum Helix gives participating software verifiable identities and controlled, encrypted service connections. It brings identity issuance, credential renewal and connection controls into an integrated product that teams can reuse as their integrations change.
Operate identity
and connections together.
- Install
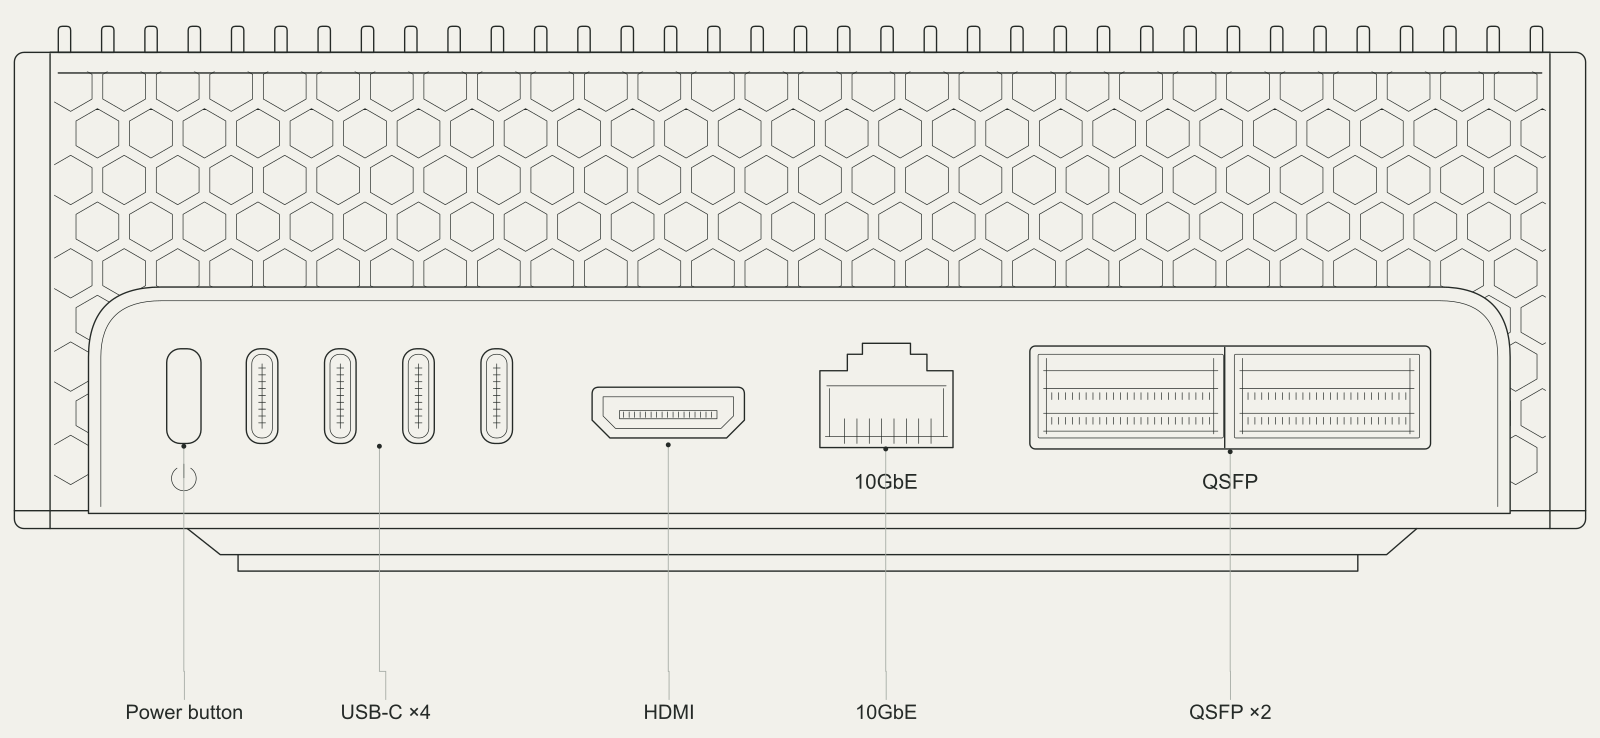
- The documented QHx Core package installs on Kubernetes using the QHx CLI or Helm, on premises, in cloud infrastructure or on deployed computing. It supplies the Manager, identity services, node agents and communication proxies alongside the applications they serve.
- Operate
- Register workloads, configure trusted authorities and set which services each identity may reach. QHx Manager configures the proxy paths; the identity services issue and renew eligible credentials. Applications using QHx Proxy do not need to implement that credential rotation themselves.
- Integrate
- Your team defines application interfaces, data formats and handling rules, and protects local connections and routes around the proxies. Application permissions, information-release decisions, infrastructure, monitoring and recovery remain your responsibility.
Change the participant.
Reuse the infrastructure.
Each new integration needs decisions about identity, service access and ongoing operation. QHx consolidates their recurring mechanisms: issuance and renewal, trusted peer identities, configured service paths and connection restrictions. Application-specific integration work remains explicit.
An existing sensor feed. A new recipient.
In this illustrative integration, an adapter reads an existing HTTP observation feed and maps it to a separately operated mission application. When the recipient changes, the publisher and its interface can stay in place.
The team reviews the adapter mapping, destination, workload registration and accepted peer identities. The issuance services, proxy mechanisms and policy structure can be reused where they remain suitable, then the team validates the changed exchange.
Follow the integration example Sensor-to-command applicationsRetain signed application evidence.
With request signing enabled, optional QHx Notary can retain signed records of successful, nonstreaming AI chat-completion exchanges over HTTP. Operators configure capture levels, storage, access and retention. A signed record identifies its signer and captured content; the application’s answer still needs its own evaluation.
Capture scope and verificationProtect information
beyond the connection.
CABE adds a separate object-protection path through a client integration. A publisher encrypts information before handing it to an approved broker; the Key Service applies policy to recipients’ requests for key material. The broker can carry encrypted reports without holding their payload-decryption keys.
QHx controls who may connect to a service. CABE separately controls access to an object’s key. Neither decision replaces the information authority’s release approval, and QHx transport does not apply CABE protection automatically.
Object protection and key accessKeep essential services
close to the workload.
Run QHx alongside the applications it serves, including on deployed computing. Place the required identity and communication services locally when the application must continue without reach-back.
Continuity depends on the available local services, accepted credentials, trust and policy. Plan credential renewal, restart and recovery for the intended outage rather than assuming they share the same dependencies.
Local operation and recovery